Multi-server by design
Areas on different SQL Servers and databases coexist side by side in one application.
Windows or SQL authentication, TLS options (Optional / Mandatory / Strict),
credentials encrypted at rest, and a connection test with a readable result.
Navigation your team understands
A customer-built menu tree — folders and data areas at several levels — with accordion
behaviour and per-entry selection highlight. What each group sees is part of the
permission model, not a cosmetic setting.
Administration & audit, in-app
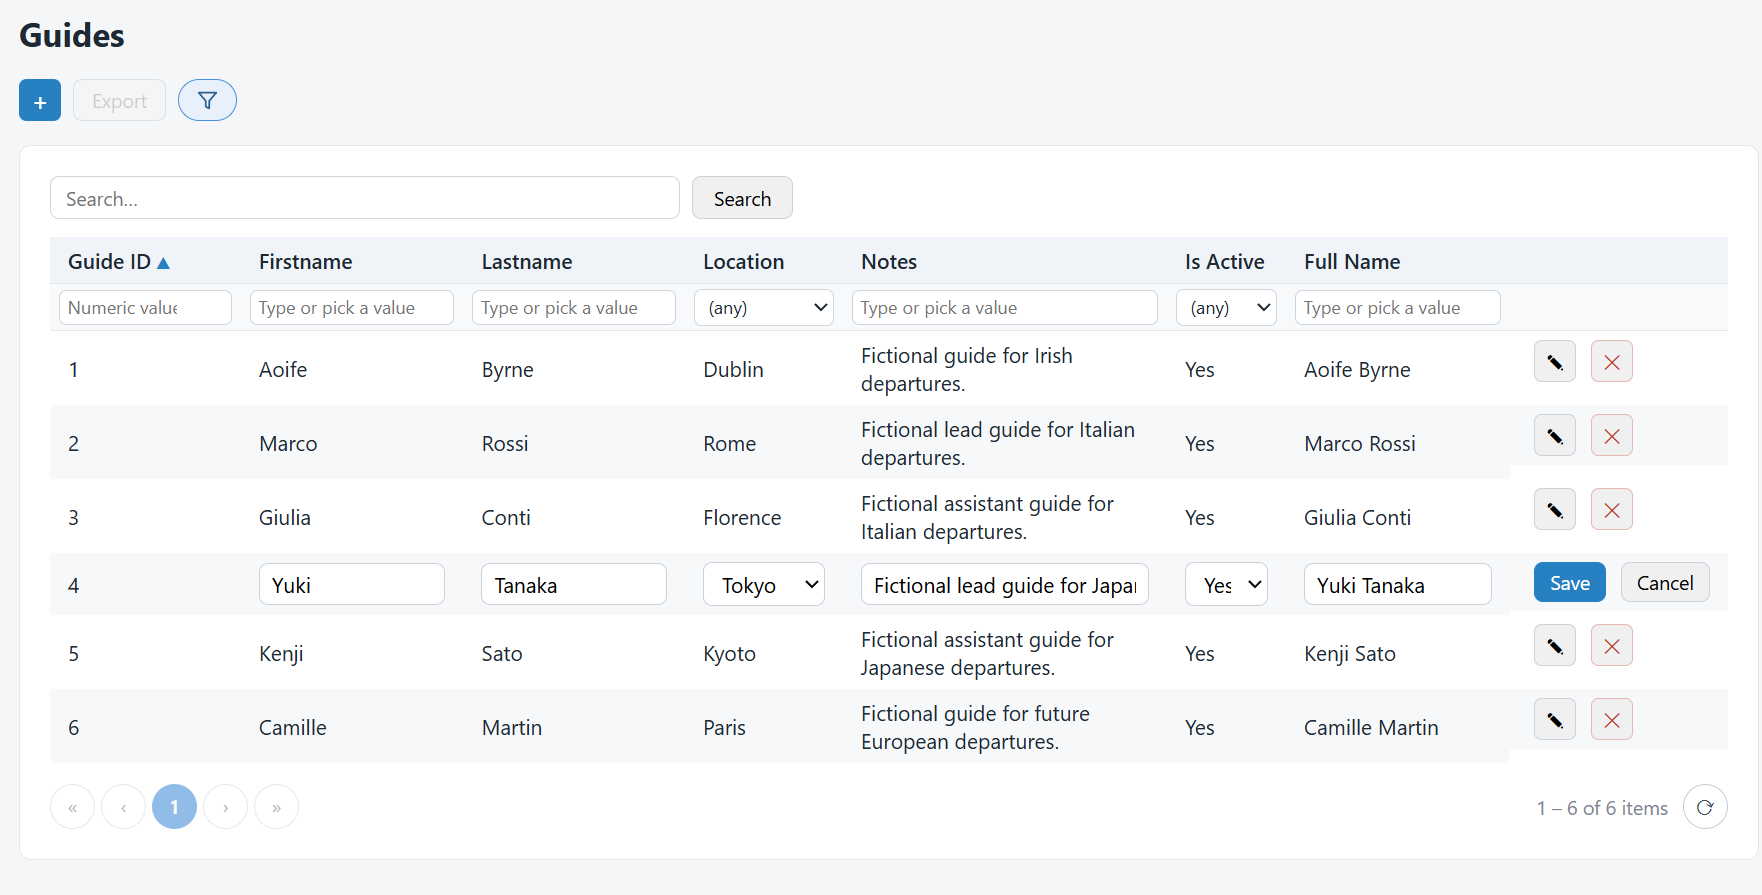
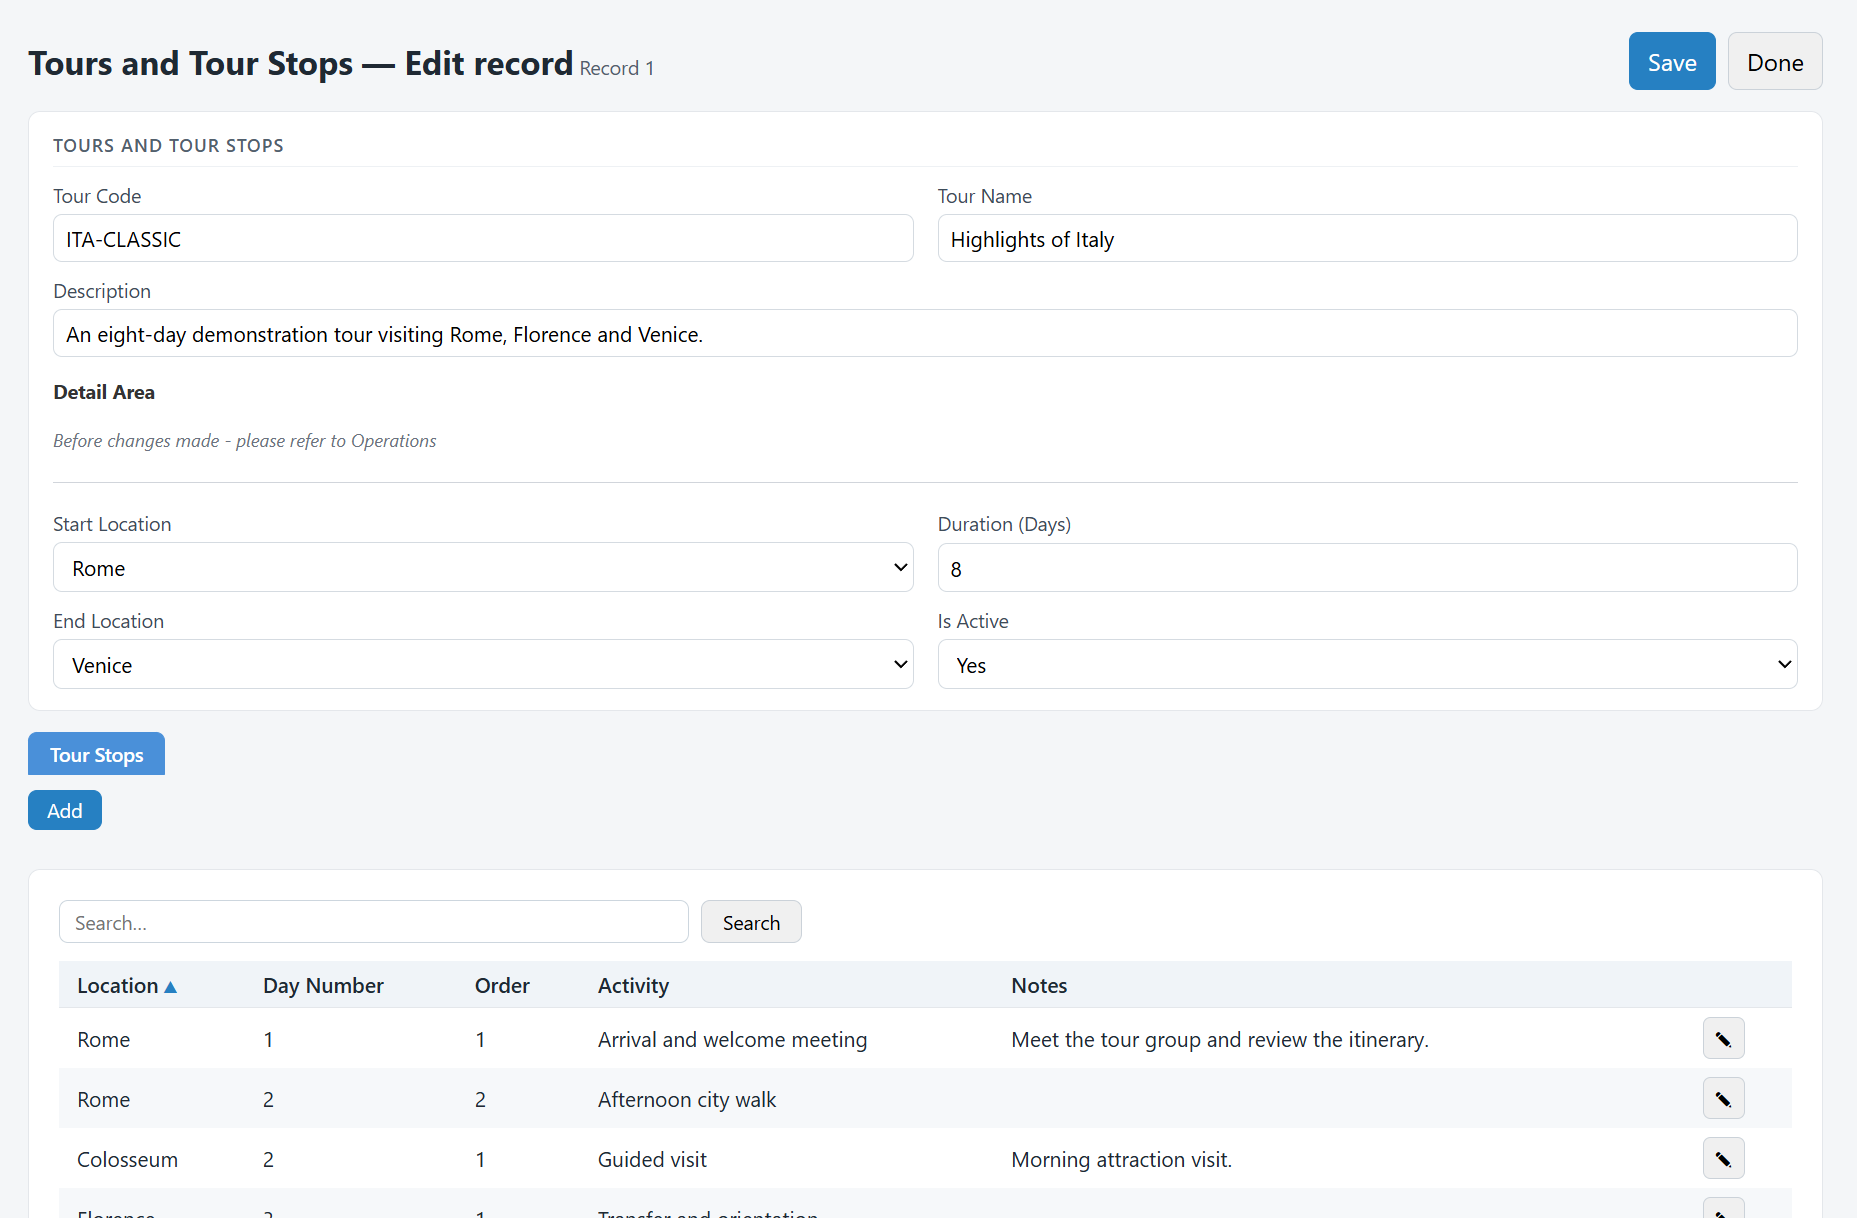
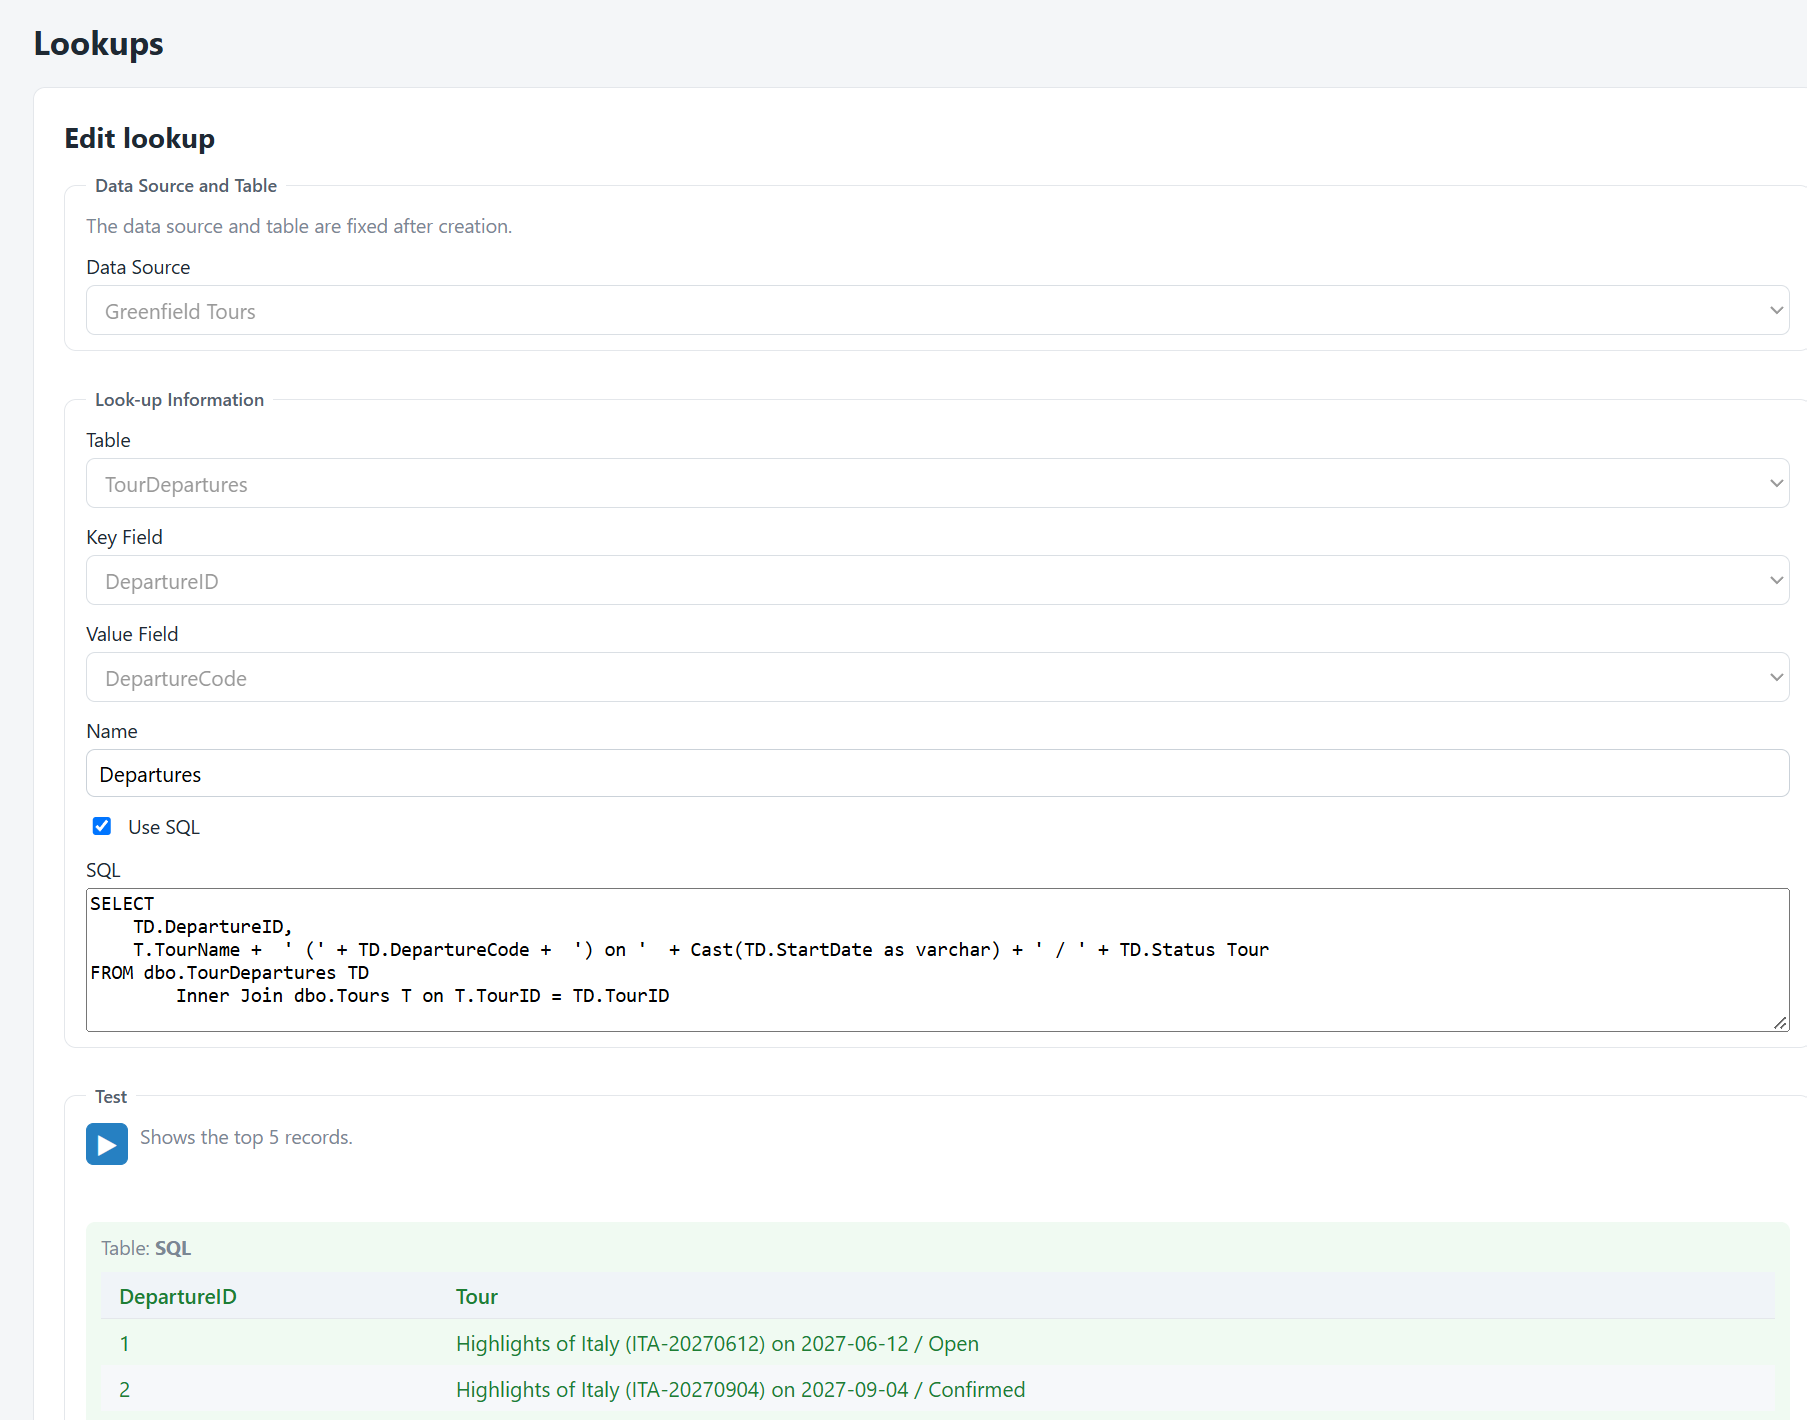
Data Sources, Lookups, Areas, Form Designs, Groups, Users and Menu are managed by your
administrators inside the application. The area editor auto-detects columns and the primary key, and
Refresh Fields re-syncs with the database when the schema moves. System Settings adds a
one-click connection health check — every data source and lookup tested, with per-item status and
response time — plus version and license information at a glance. A Data Audit log records which
user changed which records, giving your team a clear accountability trail.
Permissions that hold
User → single group → area & menu permissions, enforced server-side
in the data engine and the navigation — not just hidden in the UI. Administrators bypass;
everyone else gets a friendly, multilingual “no access” message.
Six languages, one team
The complete UI — screens, messages and hints — ships in English, Deutsch, Español,
Galego, Italiano and Português. Each user’s language is stored in their profile and
applied at sign-in. Users can also update their own password, e-mail and language in a
self-service profile — no administrator needed.
Safe by design
The application never creates or alters database structures — no DDL, ever.
Queries are parameterized, identifiers are whitelist-validated, and the browser never
sees data-source credentials. It is a guest in your database, not an owner. And there is no
AI anywhere: every result is computed deterministically on your own infrastructure.